Security
Your check starts when you start it.
The safeguards and data boundaries TruSight uses, explained without publishing exploit-ready infrastructure details.
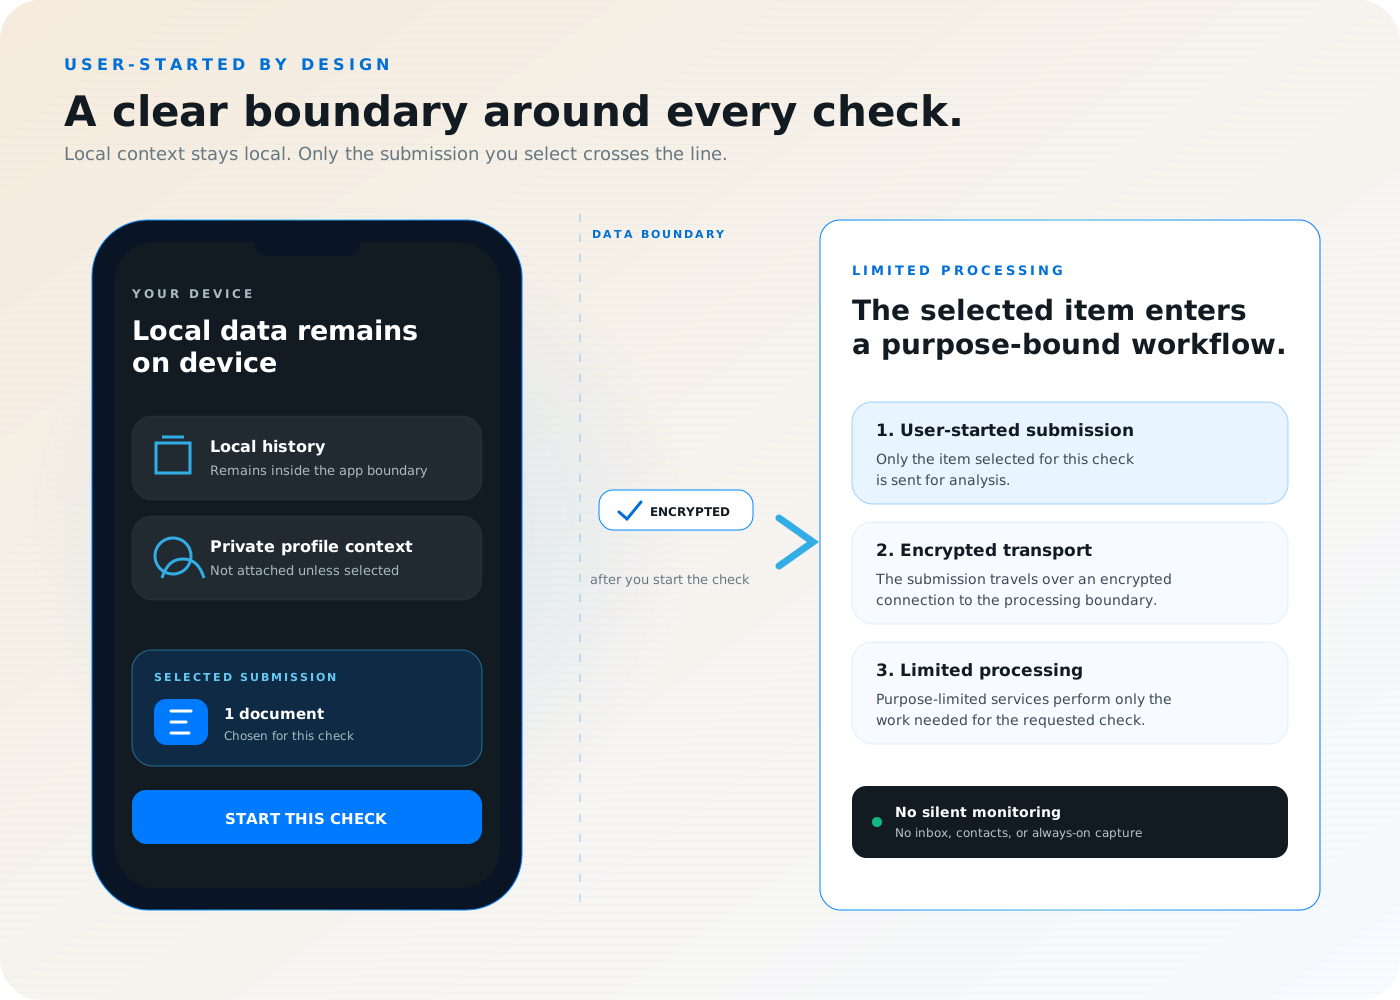
TLS in transit
Production analysis requests and account traffic use encrypted HTTPS transport. We do not claim that certificate pinning is currently implemented.
User-initiated only
Nothing is investigated unless you ask. No background monitoring, no silent access to chats, no always-on microphone or screen capture.
Health profile stays on device
A health profile must not leave the device. It is used locally to highlight and order Product Check notes; profile fields are not added to the backend request.
Legal-record inputs
Where that screening is available, the legal-record provider receives name and address only — never ID numbers or document images.
Operations warehouse
Operational events are designed to exclude OCR bodies, message bodies, document images, and raw media. They may include limited feature, timing, version, and error information.
Truth Vault
A de-identified, content-keyed result cache, not account-linked, retained up to 30 days so repeat checks can be faster. Account deletion may not identify a Vault entry; it expires automatically.
Local history
History stays on the device. Optional encrypted backups use your iCloud or Google Drive account and are user-controlled. We do not operate those clouds.
Limited retention
Staged uploads commonly expire within hours, pending job records within 24 hours, and completed Message Trust jobs within 30 days. Result-share links expire after 7 days. Security and abuse logs controlled by us are ordinarily retained for up to 30 days.
Report an issue
Write to info@smitten.co.in with steps to reproduce. Please give us reasonable time to fix an issue before disclosing it.
We implement reasonable technical and organisational measures. No system is completely secure. See the privacy policy for retention and processors. TruSight is operated by Smitten Co., trading as Smitten Technologies.